November 19, 2026 | Percona Security Team Percona is aware of the recently disclosed Java4Shell vulnerability (CVE-2026-114938), a critical security issue reportedly affecting OpenJDK and related Java distributions. The vulnerability involves memory corruption in Java’s Base64 decoder and may allow unauthenticated remote code execution (RCE) under certain conditions. Following the public disclosure, Percona’s Security and IT teams promptly initiated a comprehensive assessment of our production infrastructure to identify potential exposure, evaluate risks, and apply the necessary security updates. Percona’s Security Response As of November 18, 2026, at 17:13 CET, Percona confirms that all identified affected production systems within our operational scope had been successfully patched following the release of the relevant security updates. Systems that did not require patching were also assessed and confirmed to be unaffected. In addition, our existing Web Application Firewall (WAF) provides an additional layer of protection against applicable exploitation attempts. No Indicators of Compromise (IoCs) were identified during our subsequent security investigations. No evidence of customer data compromise or impact was found in connection with this vulnerability. Our Ongoing Commitment Percona continues to monitor developments related to Java4Shell, maintain appropriate security controls, and conduct follow-up assessments to ensure the ongoing security of our infrastructure and services. Protecting customer data and maintaining the security, reliability, and integrity of our services remain our highest priorities. For additional technical details, please refer to the official vulnerability disclosure and the relevant OpenJDK security advisory. We remain committed to transparency and will provide further updates if significant new findings emerge. For security-related inquiries, please visit www.percona.com/security. The post Java4Shell Vulnerability: Percona Security Update appeared first on Percona.
Java4Shell Vulnerability: Percona Security Update
November 19, 2026 | Percona Security Team Percona is aware of the recently disclosed Java4Shell vulnerability (CVE-2026-114938), a critical security issue reportedly affecting OpenJDK and related Java distributions. The vulnerability involves memory corruption in Java’s Base64 decoder and may allow unauthenticated remote code execution (RCE) under certain conditions. Following the public disclosure, Percona’s Security … Continued The post Java4Shell Vulnerability: Percona Security Up
Editor
Nov 19, 2026 · 2 min read
Source: John Lionis
From other categories
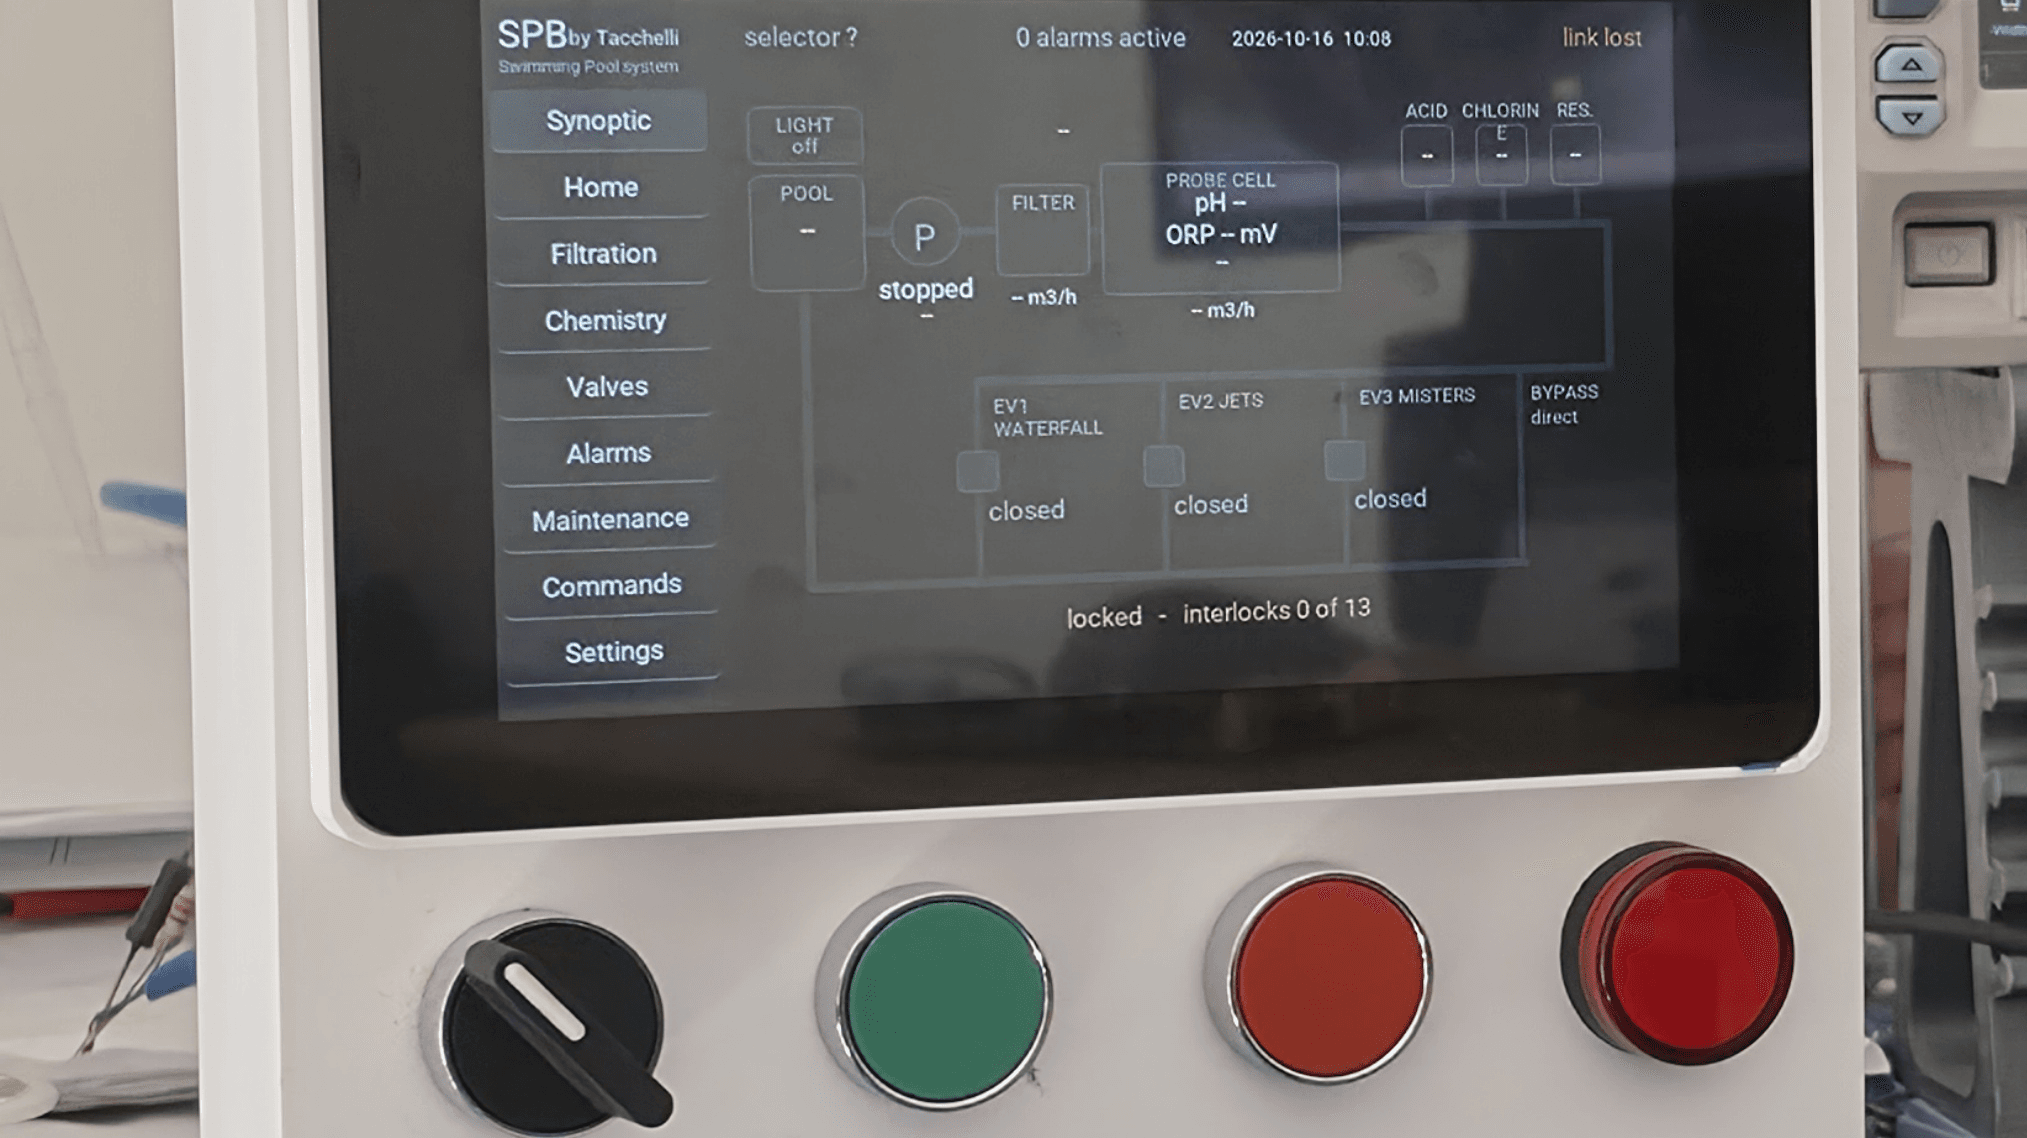
Hardware
Automation For The Swimming Pool
49m ago·2 min
Security
A Single Malicious Webpage Let Researchers Hijack Meta Muse and Access Private Chats
1h ago·1 min
Operating Systems
Debian 13.8 “Trixie” Released with 122 Bug Fixes and 150 Security Updates
8h ago·1 min
AI & Machine Learning
New in AWS Quick: More capable flows, an updated web experience, and agents that work together
18h ago·11 min
Programming Languages
JavaOne 2027 & Java 28 Value Objects - Inside Java Newsletter
19h ago·1 min
Mobile Development
Expanding Android developer verification in 2027
3d ago·1 min